Summary: A series of reported cyberattacks targeting small Non-Banking Financial Companies (NBFCs) in India has raised serious concerns about financial-sector cybersecurity, with media reports dated 29 October 2026 estimating losses of approximately ₹300 crore over two months and nearly 150 fraud complaints or cases. The reported incidents highlight vulnerabilities associated with digital lending systems, payment application programming interfaces (APIs), compromised credentials, unauthorised fund transfers and increasingly sophisticated cybercriminal techniques. Reports also describe individual incidents involving substantial financial losses, while CERT-In cybersecurity advisories issued in October 2026 have highlighted threats involving financial-sector technology systems and AI-assisted malicious activities. However, the reported aggregate losses and case counts should not be interpreted as independently audited or officially consolidated figures. For NBFCs, the developments underline the importance of strong access controls, transaction monitoring, vendor oversight, fraud prevention mechanisms and prompt incident reporting. Applicable Reserve Bank of India directions, CERT-In requirements and other statutory obligations must be assessed according to each institution’s regulatory classification and activities. Auditors and compliance professionals should pay particular attention to unusual disbursements, suspicious changes in payment instructions, weak maker-checker controls, API security and reconciliation discrepancies. The reported incidents demonstrate why cybersecurity must be treated as an essential component of financial governance, operational risk management and customer protection rather than merely an information technology function.
- 1. Reported ₹300 Crore Cyber Fraud: What Is Known?
- 2. Individual NBFC Cyber Fraud Incidents
- 3. CERT-In Warnings on Financial-Sector Cybersecurity
- 4. How AI-Assisted Cyberattacks Can Affect NBFCs
- 5. RBI and Regulatory Compliance Requirements
- 6. Cybersecurity Controls NBFCs Should Strengthen
- 7. Implications for Auditors and Compliance Professionals
- 8. What Should an NBFC Do After Detecting a Cyberattack?
- Conclusion
1. Reported ₹300 Crore Cyber Fraud: What Is Known?
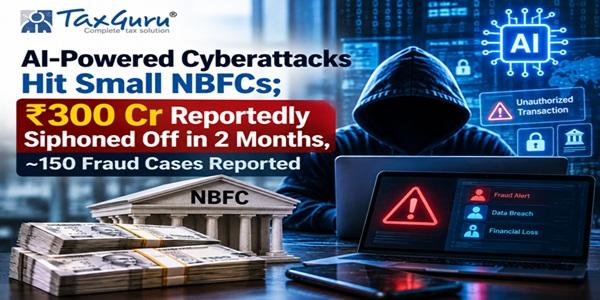
Media coverage dated 29 October 2026 reports that small NBFCs have been targeted by cybercriminals, with estimated losses reaching approximately ₹300 crore over a two-month period and nearly 150 fraud cases or complaints.
The Economic Times and Moneycontrol have reported on the alleged scale of these incidents. The reports also describe concerns about vulnerabilities in digital financial infrastructure and increasingly sophisticated methods of unauthorised fund transfers.
The reported figures should be treated as estimates attributed to investigative or industry sources. They do not establish that every reported incident involved artificial intelligence or that the aggregate loss has been independently verified.
2. Individual NBFC Cyber Fraud Incidents
According to the reporting discussed above, a Delhi-based NBFC allegedly experienced separate attacks involving approximately ₹7.5 crore and ₹7.25 crore.
A separately reported Hyderabad incident involved alleged unauthorised loan disbursements totalling approximately ₹3.3 crore across 183 transactions.
These examples indicate the potential financial impact of compromised lending or payment processes. However, they should not automatically be assumed to form part of the reported ₹300 crore aggregate unless the underlying investigations establish that connection.
3. CERT-In Warnings on Financial-Sector Cybersecurity
CERT-In advisories reported in October 2026 highlighted cybersecurity threats involving financial-sector systems, including risks associated with compromised payment APIs, stolen credentials and unauthorised transactions.
Separate warnings concerning malicious AI-assisted activities underscore how automation can increase the speed and sophistication of certain cyberattacks.
These advisories support the broader concern about cybersecurity threats. They do not, by themselves, verify the total losses attributed to the reported NBFC incidents.
4. How AI-Assisted Cyberattacks Can Affect NBFCs
Potential methods include AI-generated impersonation, sophisticated phishing, compromised employee credentials, manipulation of payment instructions and exploitation of weaknesses in technology integrations.
Digital lending platforms may be particularly exposed where loan approval, disbursement and payment systems rely on automated processes without sufficiently independent checks.
The precise attack method in each reported case remains subject to investigation.
5. RBI and Regulatory Compliance Requirements
NBFCs should assess the applicability of the RBI’s information technology governance, cybersecurity, outsourcing and fraud-risk management directions.
The RBI’s Master Direction on Information Technology Governance, Risk, Controls and Assurance Practices, 2023, effective from 1 April 2024, provides an important framework for regulated entities within its scope.
Institutions should also evaluate applicable CERT-In incident reporting requirements, preservation of electronic evidence, customer protection obligations and relevant statutory reporting requirements.
Not every cybersecurity incident is automatically classified as a regulatory fraud. The classification depends on the facts and governing directions.
6. Cybersecurity Controls NBFCs Should Strengthen
-
Enforce multifactor authentication and tightly control privileged access.
-
Apply maker-checker approvals to loan disbursements and high-value transfers.
-
Independently verify beneficiary account changes.
-
Monitor unusual API activity, transaction patterns and login behaviour.
-
Conduct regular vulnerability assessments and security testing.
-
Review technology vendors, outsourced lending platforms and contractual security obligations.
-
Maintain incident response procedures, audit trails and secure backups.
-
Train employees to identify phishing, deepfake impersonation and suspicious payment requests.
7. Implications for Auditors and Compliance Professionals
Auditors and compliance teams should examine whether internal controls adequately prevent and detect unauthorised financial transactions.
Relevant areas include bank reconciliations, loan disbursement controls, system access logs, third-party integrations, unusual ledger entries, suspicious reversals and unexplained suspense balances.
Where a material incident occurs, management must assess its financial reporting consequences, potential recoverability, regulatory reporting requirements and any implications for internal controls.
8. What Should an NBFC Do After Detecting a Cyberattack?
An affected NBFC should promptly contain the incident, preserve electronic evidence, coordinate with banks and technology service providers, and activate its incident response procedures.
Appropriate notifications should be made to law-enforcement authorities, CERT-In, RBI and other stakeholders where applicable under the governing requirements.
The institution should also assess the cause, financial impact, control failures and remedial action necessary to prevent recurrence.
Conclusion
Reports of approximately ₹300 crore in alleged cyber fraud affecting small NBFCs highlight a serious emerging financial-sector risk. Although the aggregate figures require independent confirmation, the reported incidents and official cybersecurity warnings justify urgent attention.
For NBFCs, effective cybersecurity depends on management accountability, strong transaction controls, secure technology integrations, continuous monitoring and timely incident response. AI-assisted fraud makes these safeguards increasingly important.
Sources for editorial verification: The Economic Times and Moneycontrol reports dated 29 October 2026, CERT-In cybersecurity advisories, and applicable RBI directions.
Disclaimer: This article is intended for general informational and educational purposes concerning cybersecurity, financial fraud and regulatory compliance in the Indian non-banking financial sector. The figures of approximately ₹300 crore in reported losses and nearly 150 fraud cases or complaints are based on media reports and information attributed to investigative or industry sources. They have not been independently audited or verified by the publisher against a consolidated official regulatory or law-enforcement statement. Individual incidents mentioned in this article are based on reported allegations and should not be treated as final findings of criminal wrongdoing or established financial losses unless confirmed through appropriate proceedings. References to AI-assisted cyberattacks, phishing, compromised credentials, payment API vulnerabilities and other methods describe potential cybersecurity risks and do not establish the precise technique used in every reported incident. CERT-In advisories concerning cybersecurity threats should not be interpreted as independent confirmation of the aggregate financial losses. Regulatory requirements applicable to NBFCs vary according to their classification, size, activities and relevant statutory provisions. Readers should independently examine current RBI directions, CERT-In requirements and other applicable laws before determining their compliance obligations. Nothing in this article constitutes legal, auditing, cybersecurity or financial advice. Institutions affected by suspected fraud should obtain appropriate professional assistance and follow applicable reporting and incident response procedures. The publisher does not accuse any identified institution, employee, service provider or individual of wrongdoing and makes no guarantee concerning the accuracy or completeness of the reported allegations or the effectiveness of any suggested preventive measures.